Many CEOs believe having an incident response plan signals strength, but the reality is that plans can become ineffective the moment they are left untested, out of date, or disconnected from executive decision-making. In the high-pressure landscape of Q4, when regulatory deadlines and business cycles peak, a CEO-led tabletop exercise is the most effective way to validate whether your organization is truly prepared to respond to a major incident.
A properly structured tabletop exercise exposes hidden vulnerabilities—such as unclear decision paths, outdated contacts, or unrealistic recovery timelines—before a real crisis unfolds. For SMB and mid-market organizations, this test drives essential clarity about who acts, who communicates, and how business continuity is achieved under stress. At Teremark CIO, we routinely guide CEOs through these exercises, ensuring leadership teams do not enter the year’s most critical quarter with false confidence.
If your executive team has not recently walked through a simulated incident—including legal, communications, and operational decisions—Q4 is the optimal time to close this gap and protect your organization’s resilience.
What Is a Tabletop Exercise? (Definition)
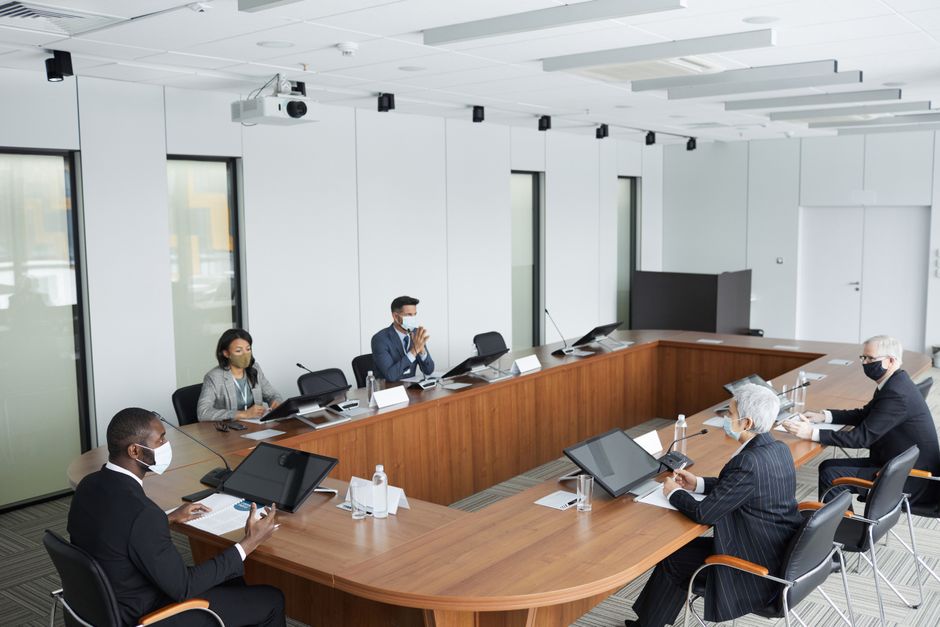
A tabletop exercise is a structured, discussion-based simulation in which key leaders walk through a realistic incident scenario. Rather than running a live technical drill, participants discuss their decisions step by step as the hypothetical situation unfolds. The goal is to identify gaps in the incident response plan, decision authority, communication strategies, and business operations that could be exposed during a real crisis.
For CEOs, tabletop exercises are the best forum to surface uncertainties about executive escalation, customer messaging, regulatory notifications, and recovery priorities—all vital to maintaining control and trust in a real incident.
Why Q4 Is the Strategic Moment for Testing
Q4 is the logical time for an executive tabletop exercise because it aligns with annual planning cycles, budget authority reviews, and regulatory compliance deadlines. Testing the incident response plan in Q4 ensures it reflects your current business structure, not last year’s organization chart or technology stack. The annual review is especially important for regulated industries and for organizations integrating significant operational changes or new vendors.
Additionally, Q4 exercises help validate whether decision-makers and escalation paths are still accurate and whether your organization can meet external notification requirements under real-world timelines. Many businesses are surprised to find their plans rely on individuals who have left the company or omit new business-critical systems added since the last review.
The CEO Tabletop: Outcomes and Critical Risks
A CEO-led incident response tabletop exercise should accomplish several core objectives:
- Surface any disconnects between IT operations, executive leadership, and board-level oversight.
- Clarify who is responsible for key decisions, such as system shutdowns, external notifications, and customer communications.
- Examine the ability to maintain business continuity while responding to the incident.
- Produce a prioritized action list for remediating gaps swiftly before year-end.
The most commonly revealed risks are:
- Unclear escalation paths
- Outdated contact lists
- Lack of authority to make emergency decisions or approve spend
- Unprepared communications for customers, the board, or regulators
- Recovery plans that do not align with business reality
Engaging outside leadership or third-party experts like Teremark CIO provides objectivity and proven structure to maximize the value of the exercise.
What a Good Tabletop Exercise Should Include
A well-run exercise is built on a clear framework. At Teremark CIO, we advise clients to ensure these core components are present:
- Defined objectives: What do you want to learn or validate? Examples include testing cross-team coordination or regulatory notification readiness.
- Realistic scenario: Choose disruptions that your business could genuinely experience, such as ransomware, business email compromise, or a third-party outage.
- Targeted participants: Include executive leadership, IT, InfoSec, legal, and critical vendors or partners. Identify actual decision-makers—do not fill the room with observers.
- Preplanned discussion prompts (“injects”): Use scripted, escalating facts that guide the group step by step and provoke focused debate.
- Clear documentation: Assign a scribe to capture all action items, gaps, and decisions for follow-up.
- Concrete after-action plan: End with remediation assignments and realistic deadlines before entering Q1.

Essential Tabletop Questions for CEOs
To drive the right insights, CEOs should ensure their tabletop exercise forces clear answers to the following:
- Who declares an incident, and how quickly?
- How is the CEO notified, and by whom?
- Who can authorize spending or engage outside counsel in real time?
- What legal and regulatory notices are required immediately?
- What is the business impact if the system is offline beyond 24 hours?
- Who crafts messages to customers and the board?
- What new data or evidence must be secured right away?
- Are roles and responsibilities updated in the written plan to match recent changes?
Step-by-Step CEO-Level Tabletop Framework
Based on leading practices and our own expertise at Teremark CIO, use this six-step framework to plan your session:
- Define the core objective: What exactly does leadership need to test or validate?
- Select one or two realistic, current risk scenarios.
- Confirm attendees: CEO, CFO, COO, IT/CISO, key legal/advisors, PR/communications, and any critical vendors.
- Prepare detailed injects, contact lists, policies, and sample communications.
- Conduct the exercise, pacing injects to reflect business urgency and escalation.
- Close with a debrief: Document lessons, create a list of action owners, and assign follow-up deadlines.
Best Scenarios for a Q4 Tabletop
For the Q4 session, pick scenarios most relevant to your business objectives and threat profile. Many organizations focus on:
- Ransomware event impacting a key system
- Business email compromise with attempted fraudulent payment
- Cloud application outage during a critical business window
- Third-party or supply chain breach announcement
- Executive credential compromise
Link scenarios to business processes and regulatory or reputational risk, not just IT systems. For more detail on choosing the right scenario, see our blog on what CEOs should look for in security leadership.
Common Weaknesses Uncovered by Tabletop Exercises
Organizations rarely fail due to a lack of technology. What we consistently uncover at Teremark CIO are process and leadership gaps. Typical issues include:
- Incident responder lists naming former employees as critical contacts
- Unverified emergency phone trees or incorrect vendor escalation numbers
- Ambiguous financial authority for emergency spending
- Customer communications draft delays
- Legal and compliance notifications created ad hoc under duress
- Recovery timelines misaligned with actual business requirements
A well-facilitated exercise by external advisors like Teremark CIO ensures these issues are not glossed over due to internal politics or wishful thinking. The after-action report then provides clear owners and deadlines for closing every gap.
What Good Looks Like by the End of Q4
After a comprehensive tabletop exercise, your company should have:
- An updated, validated incident response plan with current roles and contacts
- Documented escalation and decision paths from IT through the C-suite
- Prepared communications templates for customers, regulators, and the board
- Confirmed authority and procedures for emergency decisions
- Recovery plans with realistic, agreed-upon timelines and business impact clarity
- An actionable list of post-exercise issues, with assigned owners and deadlines for remediation
How Teremark CIO Helps CEOs Turn Insights into Action
At Teremark CIO, we partner with CEOs and boards to transform tabletop findings into tangible improvements. By providing experienced CIO, CTO, and CISO resources on a fractional, interim, or full-time basis, we help companies avoid common pitfalls and strengthen their incident response leadership without the expense of hiring permanent executives.
In addition to planning and facilitating exercises, our senior leaders guide your team through remediating gaps—aligning IT and business strategy, clarifying executive roles, and accelerating business and technology recovery plans for long-term resilience. Our objective approach ensures your Q4 preparations deliver business value, not just compliance checkboxes.
Best Practices for Tabletop Exercises
Drawing from our extensive experience, here are best practices that elevate the impact of any executive tabletop session:
- Limit participation to core decision-makers; observers slow the process and dilute focus.
- Keep exercises between 90 to 120 minutes for maximum engagement.
- Choose scenarios that are directly relevant and recent—preferably tied to real risks or incidents in your sector.
- Rehearse not only the technical recovery, but also all communications and escalation flows.
- Require each action item to have an owner and a due date; revisit open issues in executive meetings until resolved.
- Use objective, third-party facilitation to encourage candid discussions and avoid groupthink.
- Conduct after-action debriefs within 24 hours while details are fresh.
Frequently Asked Questions (FAQ)
What is the main goal of an incident response tabletop exercise?
The primary aim is to test the organization’s ability to make critical decisions, communicate effectively, and maintain business continuity during a simulated incident—surfacing any gaps in planning or leadership before a real event occurs.
Who should participate in a CEO-led tabletop?
Key decision-makers: CEO, CFO, COO/Operations, CIO/IT, CISO/Security, Legal, HR, PR/Communications, and any vital third-party vendors. The group should be small but inclusive of all essential functions.
How often should these exercises be performed?
Quarterly or at least annually—especially in Q4, before business priorities shift in the new year or before annual audits and board meetings.
What outcomes signal a successful tabletop exercise?
Clear lessons learned, immediate updates to the incident plan, ownership of remediation actions, and strengthened collaboration among executive leadership and IT/security teams.
How can Teremark CIO assist in tabletop and response planning?
By providing objective, experienced CIO and CISO leadership to design, facilitate, and help remediate tabletop findings. Our team brings practical, board-level expertise adapted to your organization’s size, sector, and risk appetite.
Should the results of table top exercises be shared with the board?
Yes—transparency with the board builds trust, demonstrates regulatory diligence, and ensures organizational alignment on how incident response capabilities will improve in the coming year.
Next Steps for CEOs and Boards
If your organization’s incident response plan has not been tested this year, schedule a CEO-led tabletop before Q4 ends. Focus on a scenario that is most relevant to your business, assemble your decision-makers, and set a firm deadline for closing the largest identified gap. For those seeking a deeper assessment of CIO, CTO, or CISO readiness, Teremark CIO’s CIO360™ IT Assessment offers a comprehensive, objective review across all core leadership dimensions.
For further guidance on strengthening your organization’s technology and security leadership heading into the next quarter, explore our recent insights including how security tool overload creates hidden risks and the case for stronger IT governance before budgeting cycles.
With decades of Fortune 500 experience and a 100% vendor-agnostic approach, Teremark CIO is prepared to help your business approach Q4, and beyond, with confidence in your readiness and resilience. If you are ready to discuss tailored leadership or want an expert eye on your incident response strategy, we are here to help.